NEWMartyn's Law framework is live

The statutory KCSIE record schools have to hold on every member of staff, volunteer and contractor — identity, right to work, DBS, barred list, references and more — as a proper online register instead of a spreadsheet on one person's laptop. Free for every school, no card, no user limit.

  • MFA-enforced access
  • Full audit of changes
  • Controlled Inspector access
  • Encrypted, password-protected exports
  • Role-based access

Built around the standards you're already asked about

UK Academy Requirements DfE Digital Standards Martyn's Law (Protect Duty) Benedict's Law (Allergy Safety) NCSC Based Security Framework NCSC Cyber Assessment Framework (CAF) ISO/IEC 27001:2022 Keeping Children Safe in Education UK GDPR Ofsted readiness Academy Trust Handbook
7
frameworks ready to use
512
requirements, each with a plain status, notes and evidence
74
key documents mapped to the items that need them
£0
for the Single Central Record, for every school
Packages

Start with the Single Central Record — free

The online SCR is free for every school, forever. The other packages are there when you're ready to go further.

FREE FOREVER

Online Single Central Record

The statutory KCSIE record as a proper online register — not a spreadsheet that lives on one person's laptop. Every check for every member of staff, volunteer, contractor and governor, with a full field-level "who changed what" audit trail.

  • Identity
  • Right to work
  • DBS & barred list
  • Prohibition & Section 128
  • Qualifications & references
  • Overseas & childcare disqualification

Plus right-to-work expiry reminders, Central Staff for people employed by the Trust across every academy, Inspector Mode for a time-boxed read-only link Ofsted can open themselves, bulk CSV import, and a password-protected export ready for inspection.

£0No card. No per-user fees. No trial clock.
INCLUDED

Inspector Mode

A time-boxed, read-only link Ofsted can open themselves, and nothing else about your account.

AVAILABLE NOW

Compliance Checklist

Self-assessment against security and governance frameworks, with Mat/Org-wide dashboards, evidence and audit trail.

NEW

Key Documents

Every framework item shows the documents that prove it. Upload each one once and attach it everywhere it is needed — 74 key documents mapped.

AVAILABLE NOW

GDPR & Data Security

Record of processing, data retention commitments, a third-party processor register with DPIA status, and DPIA documents you can upload or build from a template.

ON REQUESTMIS SYNC SOON

Single Central Record Plus+

An add-on that adds Management Information for every person: photo, mobile number, emergency contact, car registration and notes, kept separate from the statutory record, with its own password-protected export. Self-service links let staff keep their own details current, and soon staff will arrive automatically from your school's MIS, starting with SIMS.
Also: Network Tools for your IT team, and Responsible Persons (DPO, DSL, Health & Safety Lead, First Aider) COMING SOON

Why trusts use us

Everything you need to run a self-assessment, nothing you don't

One dashboard for every academy, with the detail governors and auditors actually ask for.

Add academies in seconds

Search the official DfE register by name, URN or postcode, or add a business location manually.

Mat/Org-wide comparison

See completion percentage, recent activity and open blockers across every site in your trust from one overview.

Clear maturity ladders

Every control shows exactly what "good" looks like at each level, so staff know precisely what to do next.

Track real blockers

Flag items as blocked by funding, approvals, risk or resourcing, so leadership can see where support is needed.

Evidence, attached

Attach policies, screenshots and reports directly to each control as supporting evidence for audits.

Role-based access

Trust leaders see everything; academy leads see only their own sites. Sensible permissions, by default.

Push updates trust-wide

Set a status, note or piece of evidence once and apply it to as many academies as you choose, flagged "managed by Trust".

Sign in your way

Google or Microsoft single sign-on, or a password with optional multi-factor authentication, enforceable trust-wide.

How it works

From sign-up to your first assessment in minutes

1

Create your account

Register as a business, a single academy, or a Trust. Free to get started.

2

Add your sites

Pull academies straight from the DfE register, or add locations manually.

3

Open your free Single Central Record

Switched on for every school at no cost. Add the Compliance Checklist and other packages whenever you want them.

4

Add your staff & track every check

Record each person's checks, get reminders before right-to-work permissions expire, and export an inspection-ready copy in one click.

Academy compliance

The legal duties every academy has to meet

All four are ready to use today, including Martyn's Law, ahead of its expected 2027 start.

UK Academy Requirements AVAILABLE NOW

Governance, safeguarding, data protection and wider regulatory compliance: the Academy Trust Handbook, KCSIE, UK GDPR, Ofsted readiness and more, each item linked to its official source.

DfE Digital Standards for Schools AVAILABLE NOW

The DfE's digital and technology standards: connectivity, cyber security, filtering & monitoring, and infrastructure.

Martyn's Law (Protect Duty) AVAILABLE NOW

Any site expecting 200 or more people at once must notify the Security Industry Authority and have evacuation, invacuation, lockdown and communication procedures staff know. 93 items across 15 themes, expected in force in 2027.

Benedict's Law (Allergy Safety) AVAILABLE NOW

The statutory allergy safety duty: awareness training, Individual Healthcare Plans, adrenaline devices, food allergy management and incident reporting, linked to the DfE's statutory guidance.

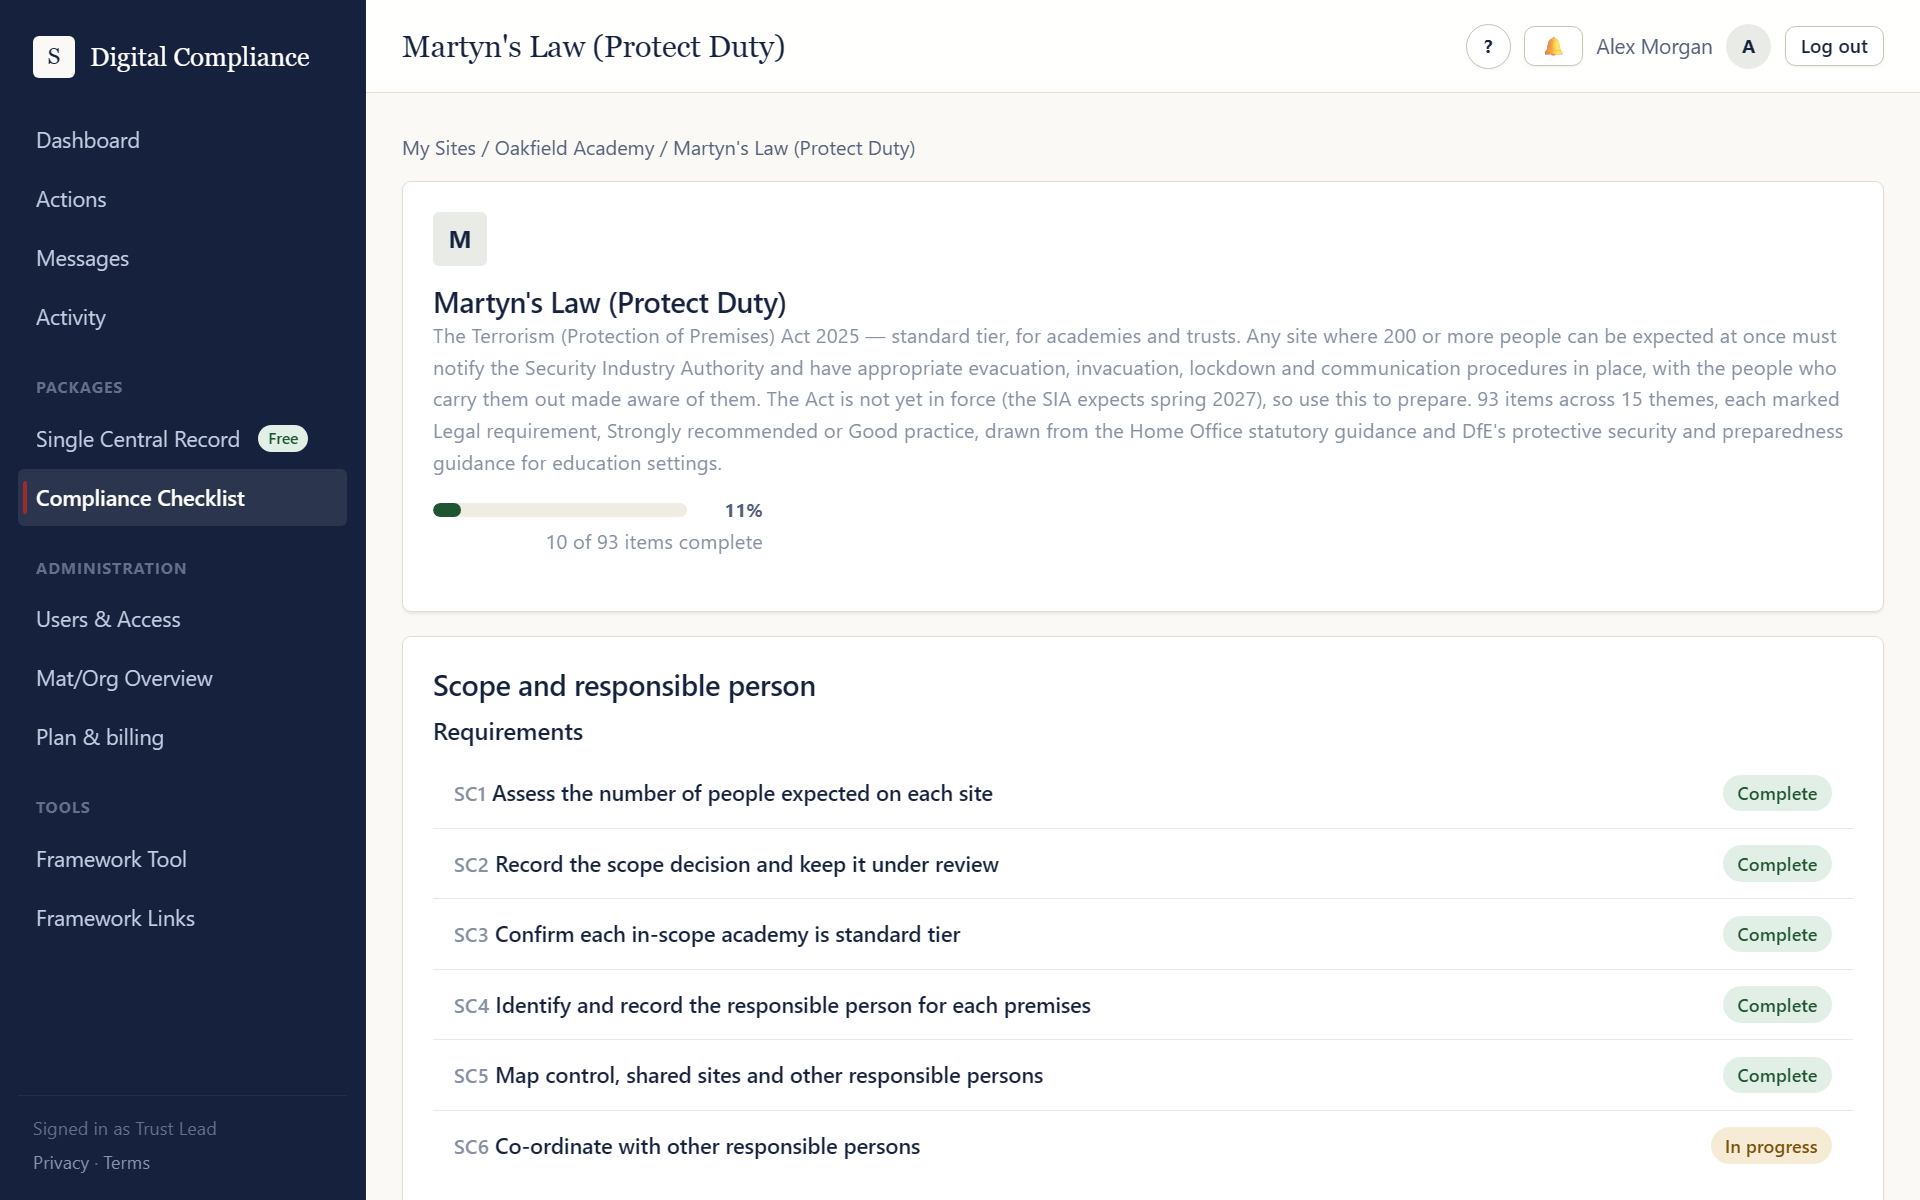
The Martyn's Law framework in Digital Compliance: a progress bar showing 10 of 93 items complete, and the Scope and responsible person theme with each requirement marked Complete or In progress.
The framework as an academy sees it: every requirement has a status, notes and evidence.
Cyber / Digital Security frameworks

Built around the standards you're already asked about

NCSC Based Security Framework AVAILABLE NOW

A maturity-based self-assessment derived from NCSC guidance, covering Organisation, People and Systems: 23 controls, 5 maturity levels each.

ISO/IEC 27001:2022 AVAILABLE NOW

All 93 Annex A controls plus the Clause 4-10 management-system requirements, on a 5-level maturity scale.

NCSC Cyber Assessment Framework (CAF) AVAILABLE NOW

The NCSC's outcome-based framework (v4.0) for assessing cyber resilience against a national-standard bar.

ISO 9001 COMING SOON

Quality management system self-assessment for trusts and suppliers.

Get your Single Central Record online — free

Set up your account and add your first site in a couple of minutes. No credit card required.